
Encrypted Variables
Encrypted variables can be used within streams or preferences to dynamically replace a key with its encrypted value. Unencrypted alternatives to these variables are Store Variables or Temporary Variables.
Variables can be applied to any node input where sensitive strings—such as tokens or authentication credentials—are required, ensuring that the actual value is never exposed in an unencrypted state.
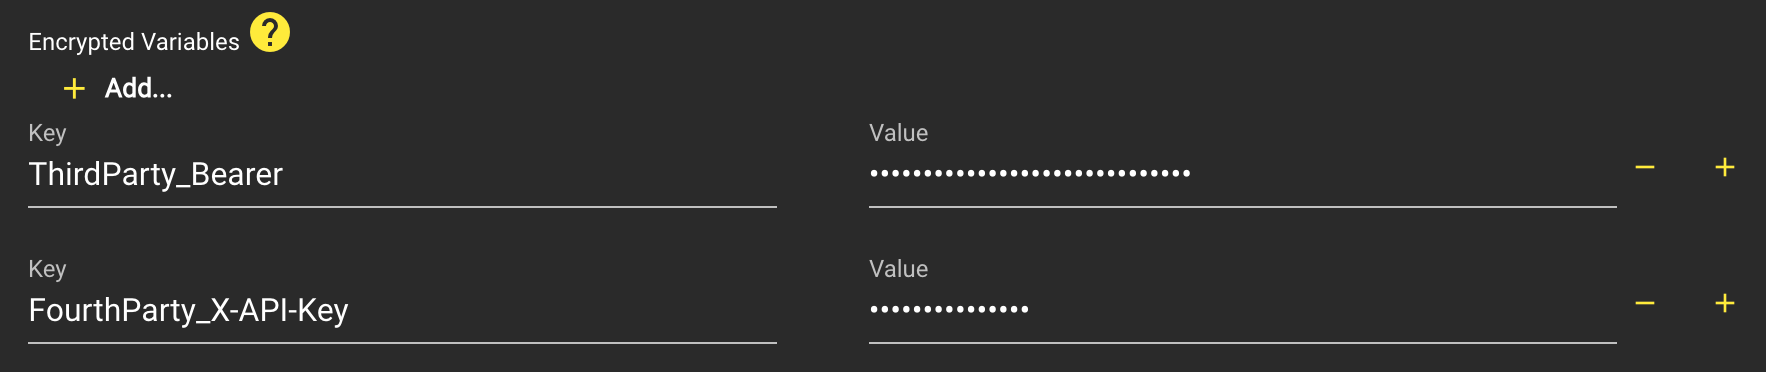
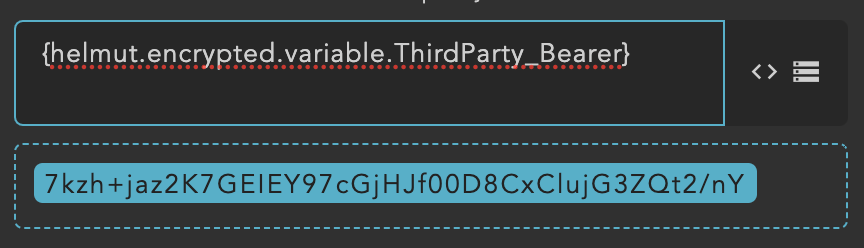
To retrieve the still-encrypted value of a key, the wildcard {helmut.encrypted.variable.?} must be used. When this wildcard is used, the value will not be displayed in plain text, making it impossible to extract the actual secret.
Set Encryption Key in Stack
Within your stack, you need to add a new parameter for the preferences container. Simply extend the existing environment configuration with:
Example
If the bearer token of a third-party application is needed for HTTP communication, an encrypted variable can be used.
The actual token value will remain hidden in both the debugger and the node configuration, while execution will still correctly resolve and use the value.
Last updated